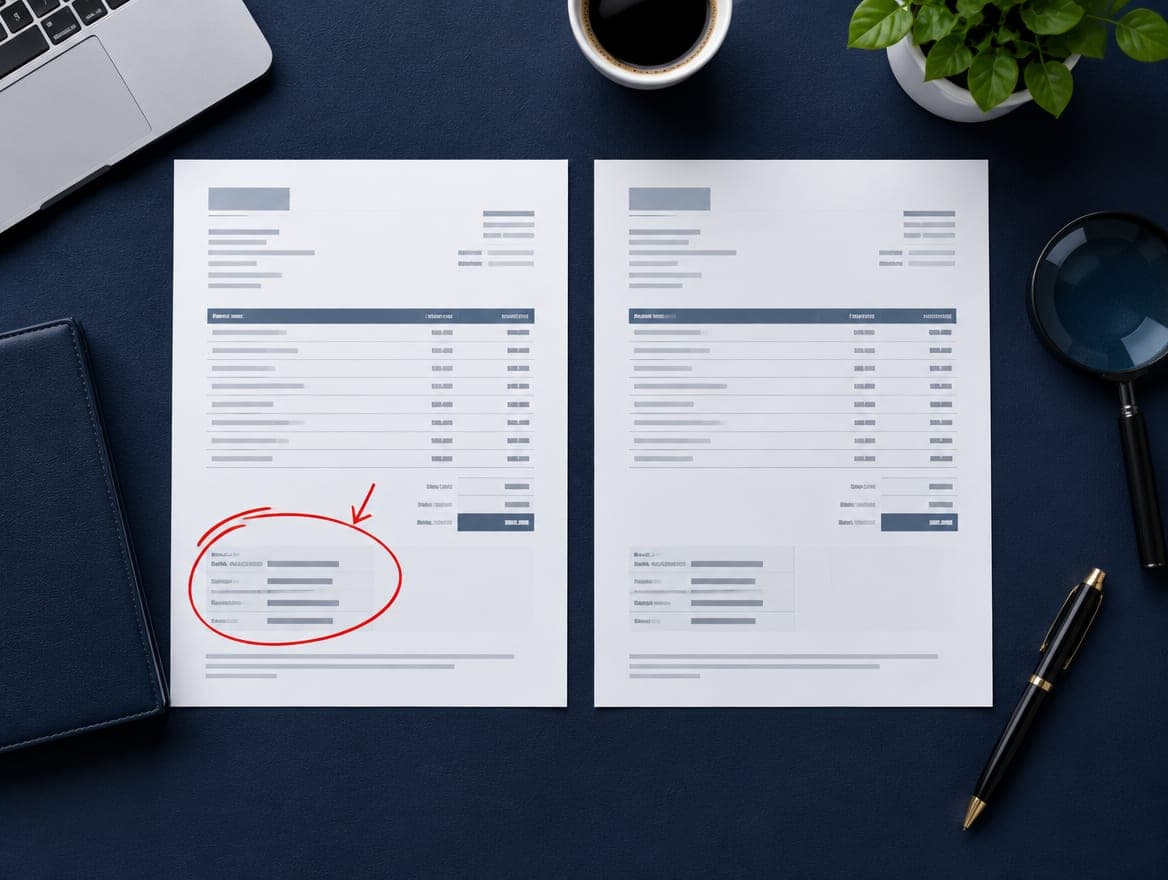
Illustrative scenario · Business email compromise
The invoice with new bank details
A company pays a regular supplier’s invoice — to new bank details sent by email. Days later, the supplier asks why they haven’t been paid.
Illustrative scenario: a composite example of a common case type — not a real client, and no real outcome is implied.
The situation
In this scenario, a finance team receives an email from a long-standing supplier, inside an existing email thread, explaining that their bank details have changed. The invoice looks exactly like previous ones. The payment is made.
When the supplier chases the unpaid invoice, both companies realise something is wrong — and each suspects the other’s email was hacked.
What made it difficult
- Time is critical if the payment is to be recalled.
- Both companies need to know whose mailbox was compromised — for insurance and liability.
- The attacker may still have access.
Our approach.
- 01
Act on the payment
The client contacts their bank immediately to request a recall, supported by a short evidence summary.
- 02
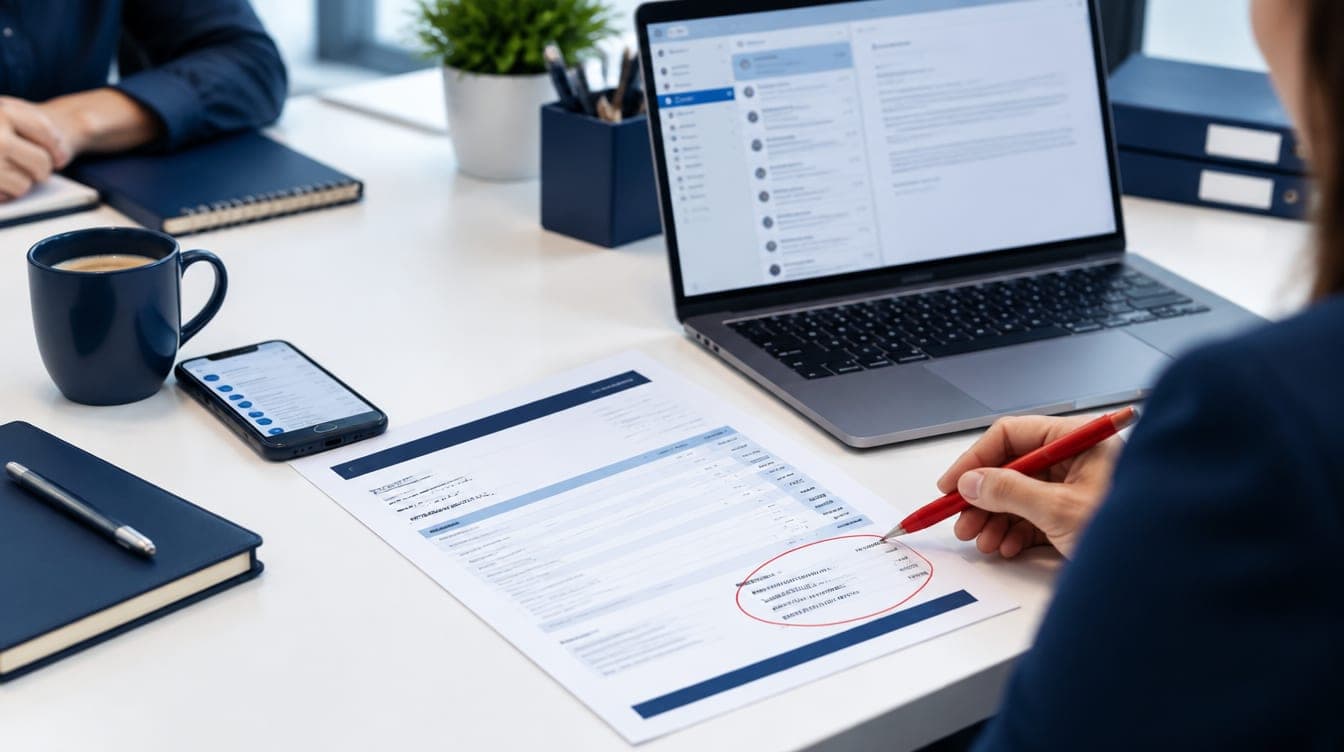
Examine the emails
Original email files and headers are analysed to establish where the fraudulent message really came from.
- 03
Review mailbox activity
Sign-in history, forwarding rules and permissions are reviewed for signs of compromise.
- 04
Close the gaps
Practical controls are recommended: phone verification of bank-detail changes, MFA and monitoring for suspicious rules.
What the client receives
- 01Email header and mail-flow analysis
- 02Account compromise findings
- 03Evidence pack for the bank and insurer
- 04Prevention recommendations
Key takeaways
- ✓Never accept bank-detail changes by email alone.
- ✓Preserve emails as original files, not forwards.
- ✓Establishing which mailbox was compromised matters for liability.
Related services
Confidential case review
Confidential case review
Tell us what happened.
Your message is read by an investigator, not a sales team. We'll reply with an honest assessment of what can be done.
Have a question first? Read our FAQ →
Prefer email? info@gfirglobal.com