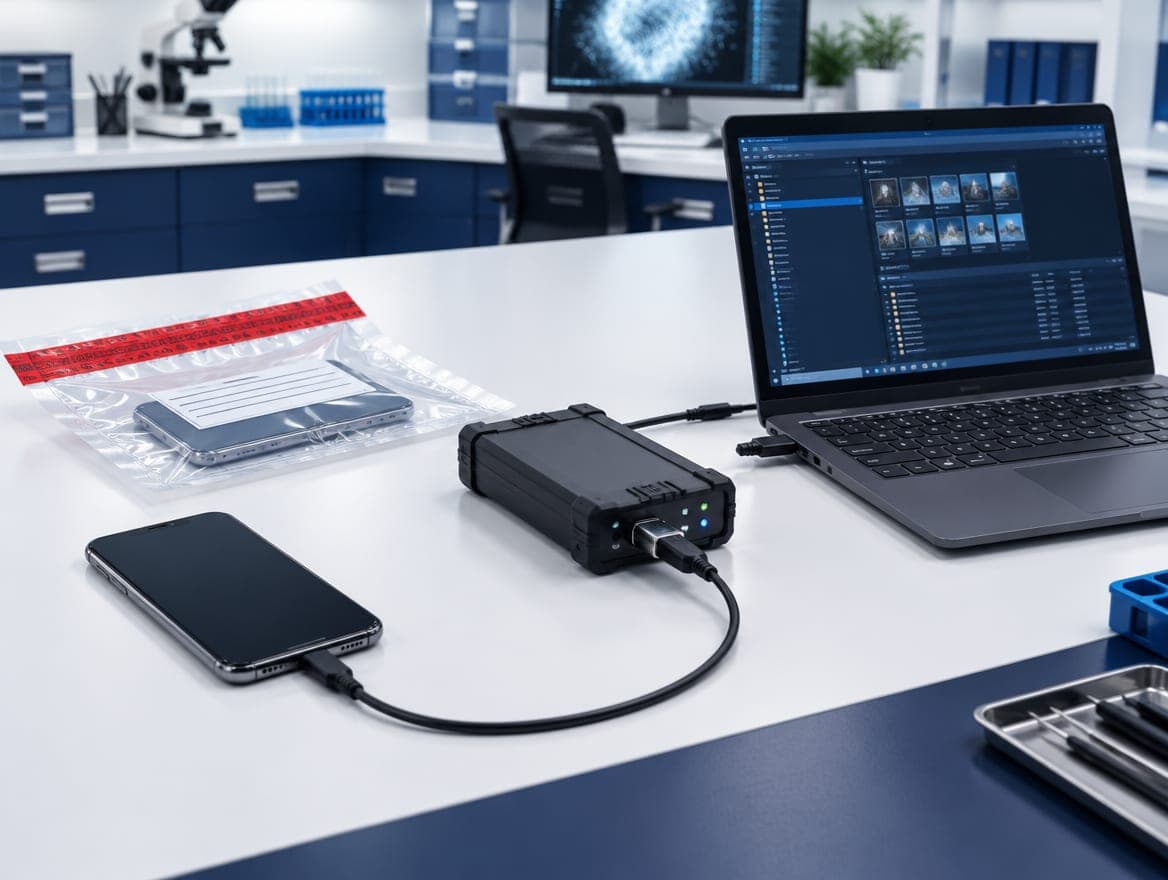
Data is captured with forensic tools that don't alter the original.
Service
Forensically sound collection and analysis of phones, computers, email and cloud accounts, preserving evidence so it can be relied upon later.
Overview
Evidence on a phone or computer is fragile. Messages can be deleted, apps updated, accounts closed — and a careless copy can change the very data you need to rely on.
GFIR collects digital evidence using forensically sound methods and documented chain of custody, so it can be trusted by lawyers, courts and investigators. We then analyse it to answer specific questions: what was communicated, when, by whom, and what happened on the device.
Whether the evidence supports a fraud claim, an employment dispute or an incident investigation, the aim is the same: findings that are accurate, reproducible and clearly explained.
Data is captured with forensic tools that don't alter the original.
Every item is sealed and logged in a chain-of-custody record.
Findings are explained in a clear expert report.
How it works
We agree exactly what needs to be established, so collection is targeted and proportionate.
Devices and accounts are captured using forensic tools, with every step logged in a chain-of-custody record.
We recover, filter and examine the relevant data — messages, files, logs, location and app activity.
A clear expert report sets out what was found, how, and what it does and doesn't show.
Who it's for
Realistic expectations
Deleted or encrypted data is not always recoverable. We assess feasibility before work begins.Before you contact us
Don't worry if you don't have everything — send what you can and we'll guide you through the rest.
Questions
Usually for a short time, or we can arrange collection in person. In some cases a remote or cloud-based collection is possible.
Sometimes. It depends on the device, the app, encryption and how much time has passed. We'll assess this before you commit.
Our process is designed to be defensible: documented methods, verified copies and a full chain of custody. Admissibility is ultimately for the court.
We only examine what's relevant to the agreed questions, store data securely and delete it according to our retention policy.
Guides
Guide · Digital forensics
Guide · Digital forensics
Guide · Digital forensics
Cryptocurrency tracing
We follow stolen or misdirected digital assets across wallets, chains and bridges, and identify where funds reached exchanges or regulated services.
Online fraud investigation
Investment platforms, impersonation and payment fraud — we reconstruct what happened and who was behind each step.
Investment fraud
Fake brokers, trading apps and ‘guaranteed return’ schemes — we document how the scheme worked and trace where your money went.
Confidential case review
Confidential case review
Your message is read by an investigator, not a sales team. We'll reply with an honest assessment of what can be done.
Have a question first? Read our FAQ →
Prefer email? info@gfirglobal.com